Unified Security. Seamless Connectivity. Secure Access from Anywhere.
Enable secure, reliable, and high-performance access to business applications, cloud services, and corporate networks regardless of where your users work. GBTECH helps organizations simplify network security, strengthen access controls, and deliver consistent protection across distributed environments.
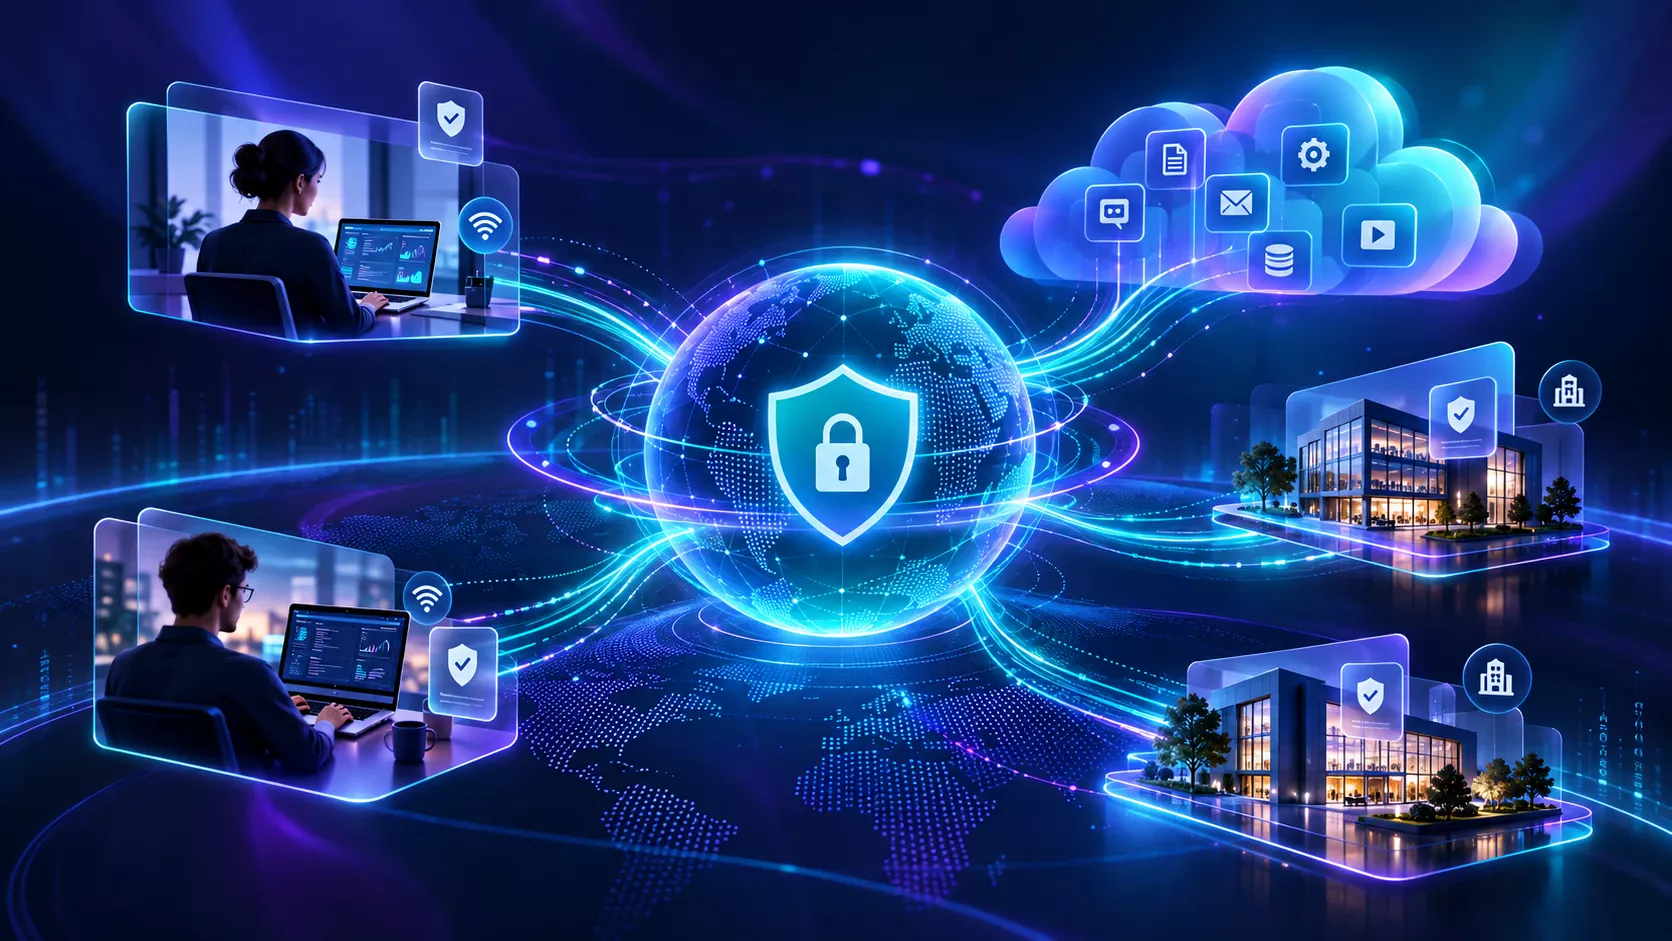
Secure access must work wherever users, devices and applications are located.
GBTECH designs SASE around practical access journeys: who is connecting, from which device, to which application and under what security conditions. Zero Trust Network Access, secure web controls, DNS security, SaaS visibility, firewall services and SD-WAN can be coordinated so distributed access is simpler to enforce and easier to observe.
Zero Trust Network Access
Provide application-level private access based on identity and context instead of exposing broad network segments through traditional VPN access. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
Secure Web Gateway
Apply web access controls and threat protection consistently for users working from offices, branches and remote locations. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
CASB & SaaS Visibility
Improve visibility into cloud application usage and apply governance where business data moves through SaaS services. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
FWaaS & DNS Security
Extend firewall and DNS-layer protections through cloud-delivered services for distributed users and sites. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
SD-WAN Integration
Combine branch connectivity and security policy so traffic can use efficient paths without unnecessary backhaul to a central location. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
Identity & Policy
Connect access decisions with identity and device context to create more consistent enforcement across distributed environments. The design is documented around ownership, dependencies and operational requirements so the capability remains supportable after implementation.
Aligning SASE with Business Operations and Infrastructure.
GBTECH evaluates the technical design, operational model and business outcome together so the service can be implemented as part of a maintainable enterprise architecture.
Apply context-aware access
Use identity, device posture and least-privilege principles to reduce reliance on broad network-level trust.
Move protection closer to the access point
Combine web, DNS, SaaS and firewall controls so security policy can be applied consistently for remote and branch users.
Connect SASE with SD-WAN and cloud
Coordinate secure access with routing and branch connectivity to reduce duplicated policy and improve user experience.
Engineering Excellence at Every Stage of Technology Delivery.
GBTECH uses a structured delivery model to reduce surprises and make technical decisions easier to understand, test and support after implementation.
Assess
Understand the current environment, requirements, dependencies and risks.
Architect
Define the target design, integration points and operational model.
Deploy
Implement through controlled change with clear documentation and ownership.
Validate
Confirm function, security and resilience against the intended architecture.
Optimize
Tune operations as usage, risks and business requirements evolve.
Discuss your sase requirements.
Share your current environment, priorities and constraints with GBTECH and we can help map a practical next step.